

Attack surface mapping is the process of identifying and cataloging an organization’s physical and digital assets, along with the attack vectors associated with them.
Cataloging here means going beyond creating an inventory of assets. It involves uncovering connections between assets and pinpointing the potential ways an attacker could interact with them (i.e., attack vectors).
In other words, attack surface mapping involves discovering all assets, attributing them to the organization, mapping asset-to-asset connections, and scanning the assets for vulnerabilities. This process is closely related to attack surface analysis.
Table of Contents
- What Are the Types of Attack Surfaces?
- Why Is Attack Surface Mapping Important?
- Attack Surface Mapping Techniques
- Tools Used for Attack Surface Mapping
- Challenges in Attack Surface Mapping
- How to Map Your Attack Surface
- How Attaxion Can Help
- Best Practices for Attack Surface Mapping
- Frequently Asked Questions
What Are the Types of Attack Surfaces?
Most organizations deal with several types of attack surfaces all at once — digital, physical, and social engineering.
- Digital attack surface: Covers every entry point within an organization’s information systems that attackers can use to gain unauthorized access, disrupt operations, or compromise the organization. It includes digital assets like websites, databases, web applications, operating systems, and cloud infrastructure, along with their misconfigurations, vulnerabilities, and other security issues. Since most of these assets can be accessed remotely, this attack surface carries a high risk of exploitation.
- Physical attack surface: This one is more restricted. It involves physical intrusion, theft, tampering, and unauthorized access to facilities, hardware, servers, data centers, Internet of Things (IoT) devices, workstations, mobile devices, and other tangible assets.
- Social engineering attack surface: This type of attack surface covers the human element and vulnerabilities that can be exploited through manipulation, such as phishing, impersonation, and pretexting.
Digital and physical attack surfaces are also split further into external and internal attack surfaces, depending on whether the assets are reachable from the public internet or only from inside the network.
From here on, this article focuses mostly on the external digital attack surface. That’s where most attack surface mapping techniques and tools apply, since they rely on scanning, querying, and fingerprinting internet-facing assets.
Internal digital assets, physical assets, and social engineering attack surfaces still need to be mapped, but they’re typically done through different methods, such as internal network scans, physical security audits, and phishing simulations, rather than the techniques covered below.
Why Is Attack Surface Mapping Important?
Attack surface mapping is the starting point for the broader external attack surface management (EASM) process. It provides the catalog that later stages, like risk scoring, remediation, and continuous monitoring, are built on. It’s also one of the early stages of both pentesting engagements and any continuous threat exposure management (CTEM) program, since penetration testers and CTEM tools alike need an accurate asset inventory before they can begin their core work.
Without mapping, security teams work blind to some parts of their organization’s environment, which is risky given that out of the 85% of global businesses that experienced security incidents, 11% are attributed to shadow IT or resources used without the IT or security department’s authorization and oversight.
Here’s a closer look at what attack surface mapping adds to a security program:
- It improves visibility into entry points: The most significant benefit of this process is improved visibility into all potential entry points for cyberattacks, including assets that may have otherwise been overlooked.
- It helps teams understand attack vectors and attack paths: Mapping goes beyond identifying individual attack vectors. It also helps organizations understand how different assets relate to each other, which can reveal potential attack paths, the “digital roads” attackers can take to move from one system to another.
- It leads to the discovery of unknown and unmanaged assets: A large share of an organization’s attack surface tends to stay hidden from IT teams — according to ManageEngine, 60% of employees admit that they are using unapproved AI tools more than they did in the previous year, and 93% are putting information into those tools without approval. Mapping brings these and other unmanaged assets into view before attackers find them first.
- It supports risk-based prioritization: With a full inventory of assets and information about how they connect, security teams can focus remediation efforts on the exposures that pose the greatest risk instead of addressing low-impact ones first.
Attack Surface Mapping Techniques
Since an attack surface comprises very different assets and issues, it’s impossible to use just one cyber reconnaissance technique to discover all of them. As a result, mapping requires a blend of techniques that mostly run automatically:
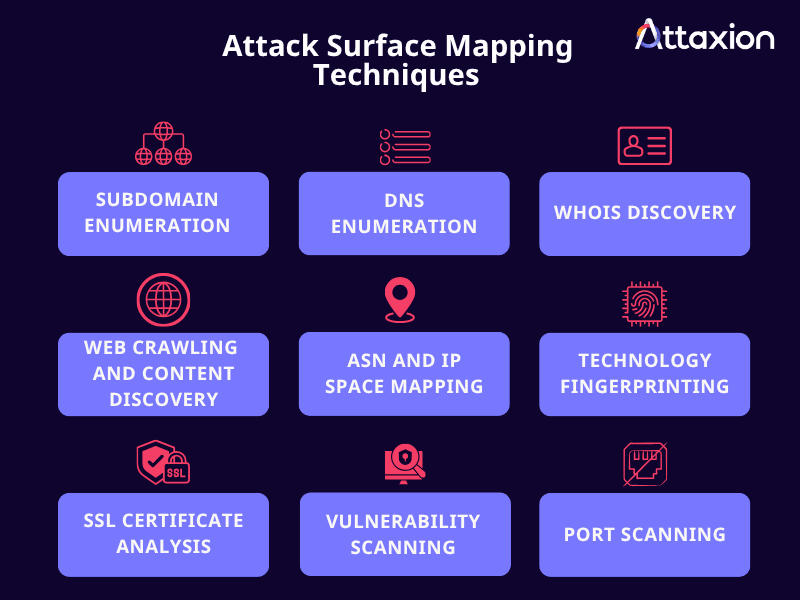
- Subdomain enumeration: This technique aims to discover all subdomains associated with a target domain so that exposed staging environments and other services are immediately detected. It’s a complex technique that can be performed directly by querying DNS servers to find subdomains (i.e., active subdomain scanning), by analyzing historical DNS data and certificate transparency logs (i.e., passive subdomain scanning), but it also benefits from web crawling, DNS bruteforcing, and more.
- DNS enumeration: Attack surface mapping requires the use of tools that can gather the DNS records associated with a domain (e.g., A, AAAA, CNAME, MX, NS, TXT). DNS enumeration tools typically query DNS servers or DNS databases to retrieve these records. Reverse DNS and Reverse IP lookups then help discover other assets associated with these records (such as other domains using the same mail server, for example). This is a signal that, combined with other similar signals from the techniques below, increases the probability that the discovered assets belong to the organization.
- WHOIS discovery: This technique identifies a domain’s ownership and registration details, which are useful for discovering other assets owned by the same organization.
- Web crawling and content discovery: This involves exploring websites and web applications by following links and submitting various HTTP requests to map the structure and discover all accessible pages, directories, files, and associated content. That helps reveal technologies used across the organization’s websites and potentially find more associated domains.
- ASN and IP space mapping: Identifying the ASNs and IP ranges associated with the organization helps security teams understand the organization’s network infrastructure.
- Technology fingerprinting: This attack surface mapping technique gives security teams insights into the organization’s tech stack, including content management systems (CMS), web frameworks, server software, programming languages, and other related software. Technology fingerprinting also extends to an organization’s cloud environment, helping identify cloud instances and assets.
- SSL certificate analysis: This technique examines SSL certificate details, such as expiration dates, certificate authority (CA) validation, and certificate chains, to detect security vulnerabilities and misconfigurations. It also extracts subject alternative names (SANs) to discover more related assets.
- Vulnerability scanning: This technique compares the asset’s software versions and configurations against known vulnerability databases to detect potential vulnerabilities. Some vulnerability scanners also check for common misconfigurations, such as weak passwords and default credentials.
- Port scanning: Port scanning determines which ports are open and what services are running on them by sending network packets.
Tools Used for Attack Surface Mapping
The techniques above are carried out using dedicated tools. Broadly, these tools fall into two groups.
Tools for Individual Techniques
There are specialized, often open-source tools built for a specific mapping technique. For example, there are tools like naabu that handle port scanning, while other tools like assetfinder or OWASP Amass focus on subdomain and IP address discovery by pulling data from certificate transparency logs and other public sources.
Similar single-purpose tools exist for DNS enumeration, technology fingerprinting, and SSL certificate analysis. Chaining several of these tools together can cover the full mapping process, but it also means more setup, more output to reconcile, and more manual work to make sure that results are always updated.
All-in-One Mapping and Scanning Tools
There are also platforms that combine various reconnaissance techniques with vulnerability scanning in one workflow. Commercial options like Attaxion are built this way.
They move automatically from asset discovery to infrastructure mapping to vulnerability detection, without requiring a security team to run and stitch together separate results.
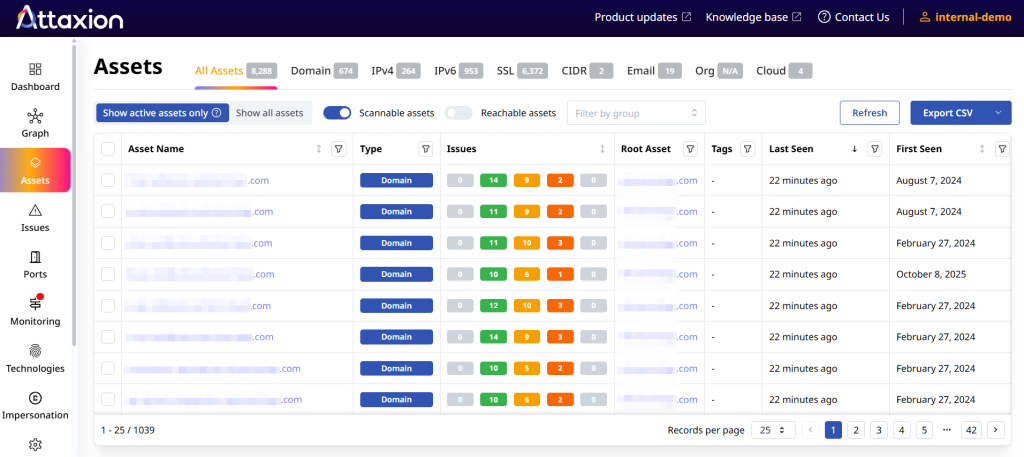
This is the approach most external attack surface management platforms take, since it cuts down on manual work and keeps the attack surface map current as the environment changes.
Challenges in Attack Surface Mapping
Some of the most common challenges teams face when mapping include:
- Complex, hybrid environments: Modern networks span multi-cloud and hybrid infrastructure, which makes it harder to get one consistent view of every asset.
- IoT devices and shadow IT: IoT devices and shadow IT assets drastically expand the attack surface and make IT infrastructure more tangled.
- A constantly changing environment: An organization’s attack surface can change and expand quickly, adding new security risks despite the best efforts of the security team.
- Manual, point-in-time efforts falling short: Taking inventory manually on a monthly or even weekly basis still leaves security gaps. Assets can become exposed and get targeted by attackers in between mapping efforts.
- Data overload without context: Mapping tools can return large volumes of assets and findings, and without prioritization, security teams can struggle to know where to focus first.
How to Map Your Attack Surface
Mapping your attack surface can be described as a five-step process, which we outline below. Most of these steps can be automated with Attaxion.
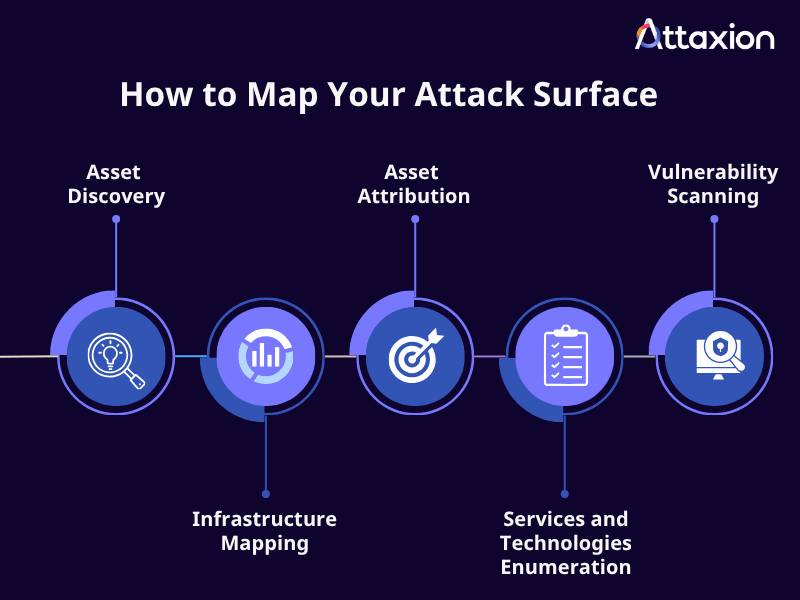
1. Asset Discovery
Asset discovery involves identifying all Internet-facing assets, specifically those that contribute to an organization’s attack surface. This step essentially tells organizations what the possible attack targets are.
Websites and web applications are the most common external-facing assets, and they are included in asset discovery. However, they are related to other assets that may not be immediately visible but nonetheless externally exposed, such as:
- Domains
- Subdomains
- IP addresses
- SSL certificates
The asset discovery process should also identify cloud instances and buckets. Email addresses can also be considered an external digital asset type since they are visible to outsiders and can be exploited in impersonation and phishing campaigns. The main goal of this step is to identify forgotten or unknown assets that have not been on the security team’s radar.
2. Infrastructure Mapping
The next step is to document network architecture, dependencies, and third-party vendor integrations to gain a clear picture of the system layout. This is called infrastructure mapping, which essentially maps asset-to-asset connections.
3. Asset Attribution
Once you know how assets connect to each other, the next step is confirming that a discovered asset actually belongs to your organization. This is important because mapping techniques may discover assets tied to shared hosting providers, CDNs, or third parties, and treating those as owned assets would produce an inaccurate map.
Security teams typically confirm ownership by cross-referencing WHOIS records, SSL certificate details, ASN ownership, reverse IP lookups, and cloud account metadata. Getting attribution right keeps the attack surface map accurate and prevents wasted effort on assets that aren’t really the organization’s responsibility.
4. Services and Technologies Enumeration
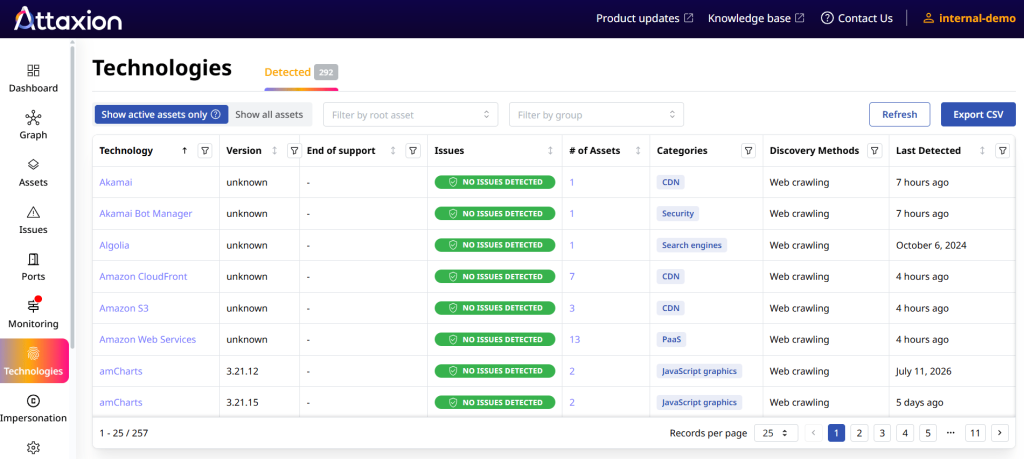
Now that you have visibility over the organization’s digital assets and how they are connected, you need to identify open ports, exposed services, software versions, and API endpoints.
It helps security teams understand how attackers can potentially gain access and make the next step — vulnerability scanning — more targeted and effective.
5. Vulnerability Scanning
Since there is already a list of services and technologies (along with their software versions), security teams can focus vulnerability scans on specific components and even perform version-specific vulnerability detection.
For instance, they can perform a targeted scan on a web server running on, say, open port 80 that was found while enumerating the organization’s services and technologies. While opening port 80 is common, the vulnerability scan revealed that the web server is running Apache HTTP Server version 2.4.41 (the latest as of the time of writing is version 2.4.68). This means that the organization’s web server is outdated and has unmitigated Apache server vulnerabilities.
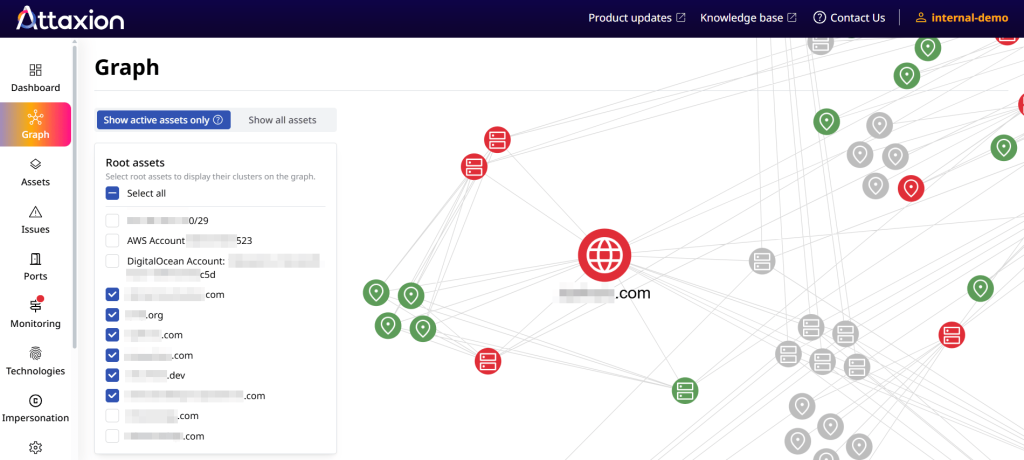
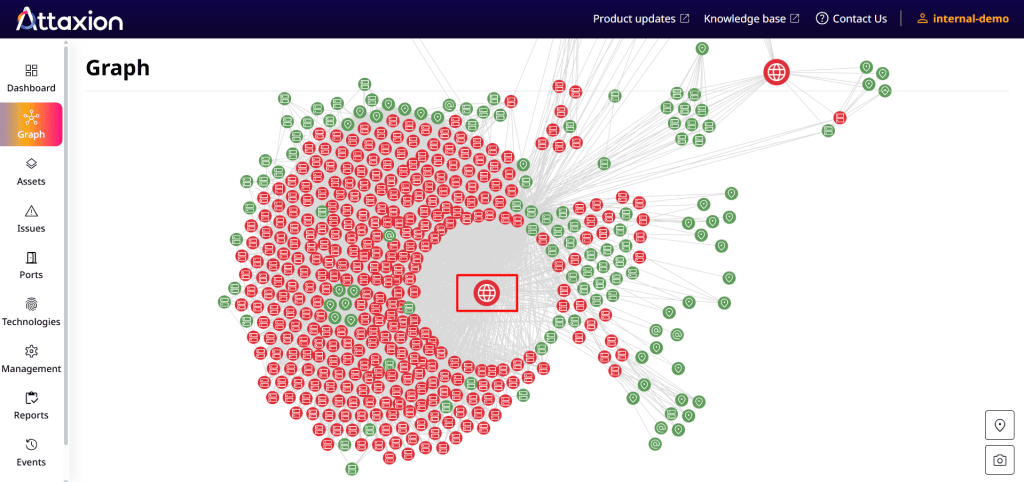
Take a look at the website inside the red box in the attack surface graph below. All of the vulnerable assets (colored red) connected to it, both directly and indirectly, represent potential attack vectors. This helps organizations understand where an attacker can start their infiltration efforts and enables security teams to map out possible attack paths.
How Attaxion Can Help
Attaxion is an exposure management platform that automates the attack surface mapping process described above from end to end. Its discovery engine combines subdomain enumeration, DNS and WHOIS lookups, ASN and IP space mapping, technology fingerprinting, and SSL certificate analysis to build a continuously updated inventory of domains, subdomains, IP addresses, cloud assets, open ports, and other assets.
The platform also handles asset attribution semi-automatically, assigning confidence scores to asset candidates based on the number and types of connections the candidate has with assets that are known to belong to the organization. It then enumerates the services, technologies, and software versions running on each one. From there, Attaxion’s Graph tab (shown on the screenshot above) turns that inventory into a visual mapping of how assets connect to each other.
Attaxion then scans all assets for vulnerabilities, giving security teams a single, unified view of the attack surface and which exposed assets carry known, exploitable vulnerabilities.
It’s worth noting that mapping is only the first step. Once you know what’s exposed, how it’s connected, and what could be vulnerable, the work shifts to attack surface analysis and then prioritizing which exposures pose the biggest risk, remediating them, and continuously monitoring the attack surface for any changes. That’s the full EASM process, and we break it down in our EASM guide.
Best Practices for Attack Surface Mapping
Having outlined the basic steps of mapping, it’s important to acknowledge that these activities can be optimized by integrating best practices.
- Start mapping from known critical assets, such as databases containing customer financial records or public login pages, so attack paths to them are found and secured first.
- Automate mapping using ASM tools that combine asset discovery and vulnerability scanners to maintain an up-to-date asset inventory.
- Use your map for threat modeling, alongside frameworks like MITRE ATT&CK that can be used to map out attacker tactics.
- Disable unused services, close open ports, and update software regularly to minimize the attack surface.