

Asset discovery is the process of finding all hardware, software, and cloud resources connected to an organization’s environment, including those that IT and security teams don’t know about. It’s the first step in building an accurate asset inventory, and it’s the foundation for vulnerability management, exposure management, attack surface management, and regulatory compliance, among other processes.
Here’s everything you need to know about asset discovery, from how it works and why it’s important to the challenges organizations face and best practices.
Internal vs. External Asset Discovery
There are two major categories of assets: internal assets, which reside within an organization’s network, and external assets, which are exposed to the internet. Although the same type of asset — for example, a server — can be either internal or external, the two categories differ significantly in how they are managed and, in particular, how they are discovered.
Internal Asset Discovery
Internal asset discovery identifies assets that are a part of the organization’s own network. One can discover them using methods like agent-based discovery or internal network scans. Internal assets are assets that are not accessible from the public internet by default. Below are some examples of internal assets.
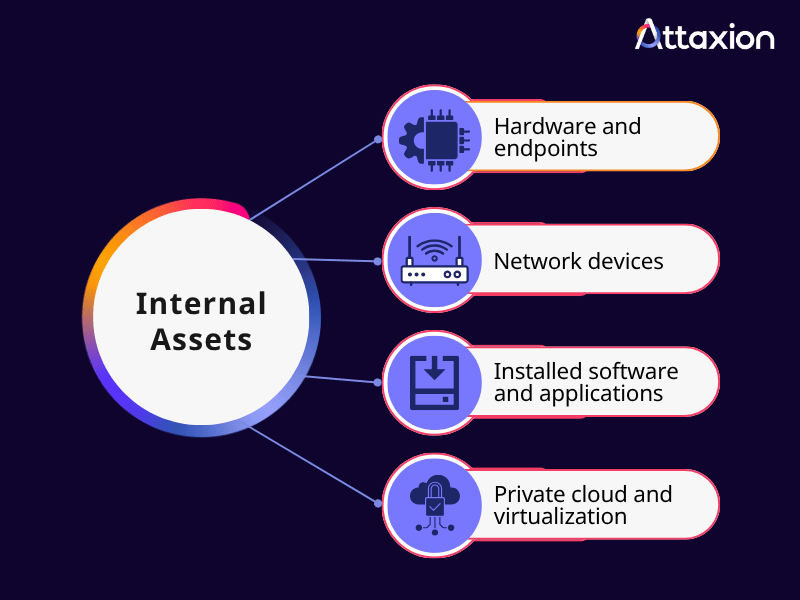
- Hardware and endpoints, such as laptops, servers, and printers
- Network devices, like routers, switches, and firewalls
- Installed software and applications
- Private cloud and virtualization infrastructure, like on-premises VMware or Hyper-V clusters used to pool physical server resources together
External Asset Discovery
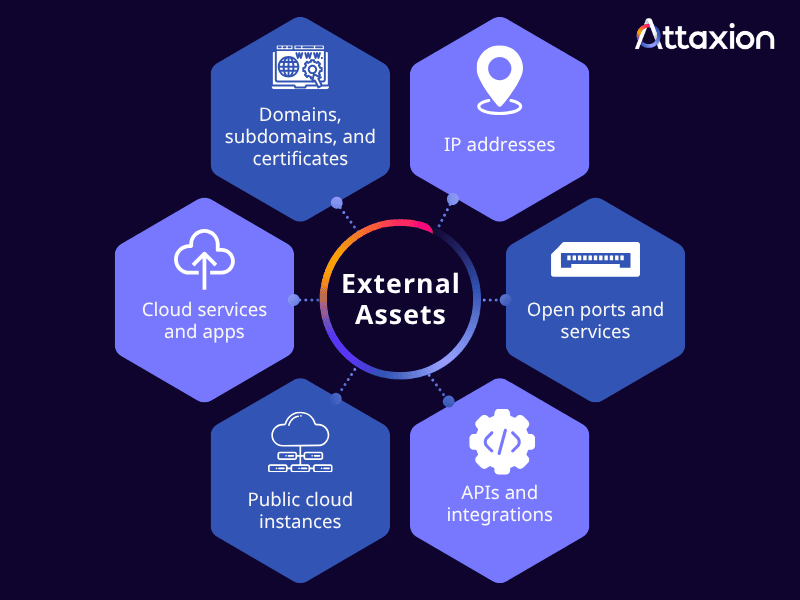
External asset discovery takes an outside-in view instead. It looks for assets exposed to the public internet, such as the following:
- Domain names, subdomains, and certificates: The public-facing domains and subdomains of an organization used to host its main website, landing pages, portals, and other publicly accessible Web-based services, along with the TLS/SSL certificates tied to them.
- IP addresses: Public IP addresses linked to external-facing systems and services, such as resolving domains and subdomains.
- Open ports and services: Internet-exposed network ports and services, such as web and email servers.
- Application programming interfaces (APIs) and integrations: APIs and integrations with publicly accessible external services.
- Public cloud instances: Organization-controlled resources hosted in public clouds, such as virtual machines (VMs), containers, and other resources hosted on platforms like AWS and Azure.
- Cloud services and applications: Third-party or managed cloud services used by different teams in the organization.
Some of them will be known, while some can turn out to be shadow IT — assets that someone has spun up without the IT department’s authorization and oversight.
External asset discovery covers the assets listed above, usually with external attack surface management (EASM) tools that run discovery continuously, since internet-facing assets change constantly as teams create new cloud instances or register new domains — things that an organization’s internal inventory can’t account for.
EASM closes that gap by scanning the internet the way an attacker would, which is often the only way to catch forgotten subdomains, unsanctioned cloud accounts, and other unknown, internet-facing infrastructure before someone else finds them.
How Does Asset Discovery Work?
Asset discovery is a cyclical process made up of several steps that most asset discovery tools run on a recurring basis.
The process below describes external asset discovery, since it starts from zero and has to build a picture from scratch. Internal discovery follows a shorter path because the tool already has access to the network and can skip straight to finding and enriching assets instead of working outward from a handful of seeds.
- Set the Scope
Start with a list of seed assets, which can be known domain names, IP ranges, or cloud accounts. This scope defines where discovery should begin and gives the tool a starting point to branch out from.
- Discover Assets
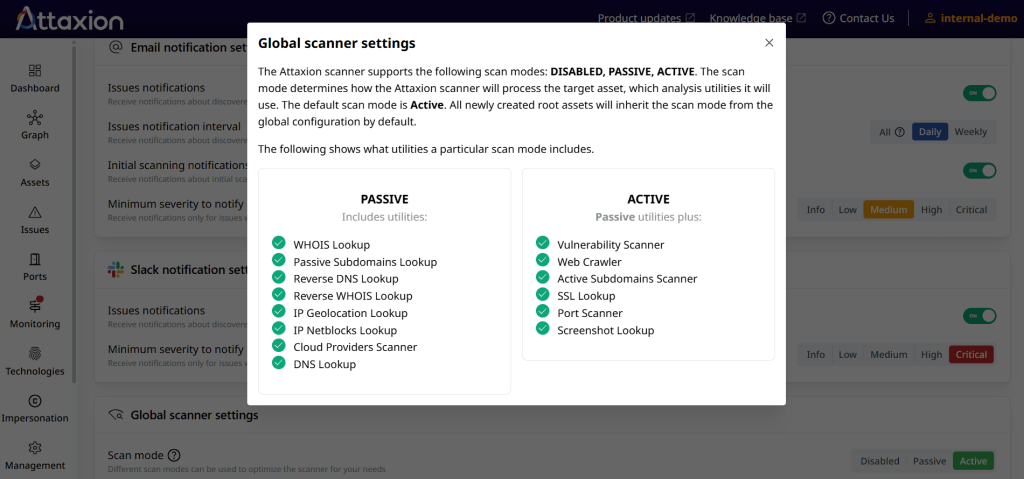
Using those seed assets as starting points, the tool looks for assets using one or more discovery methods (active, passive, agent-based, or API-based, covered in the next section). Most programs combine several methods, since each one tends to find things the others miss.
- Enrich with Additional Asset Data
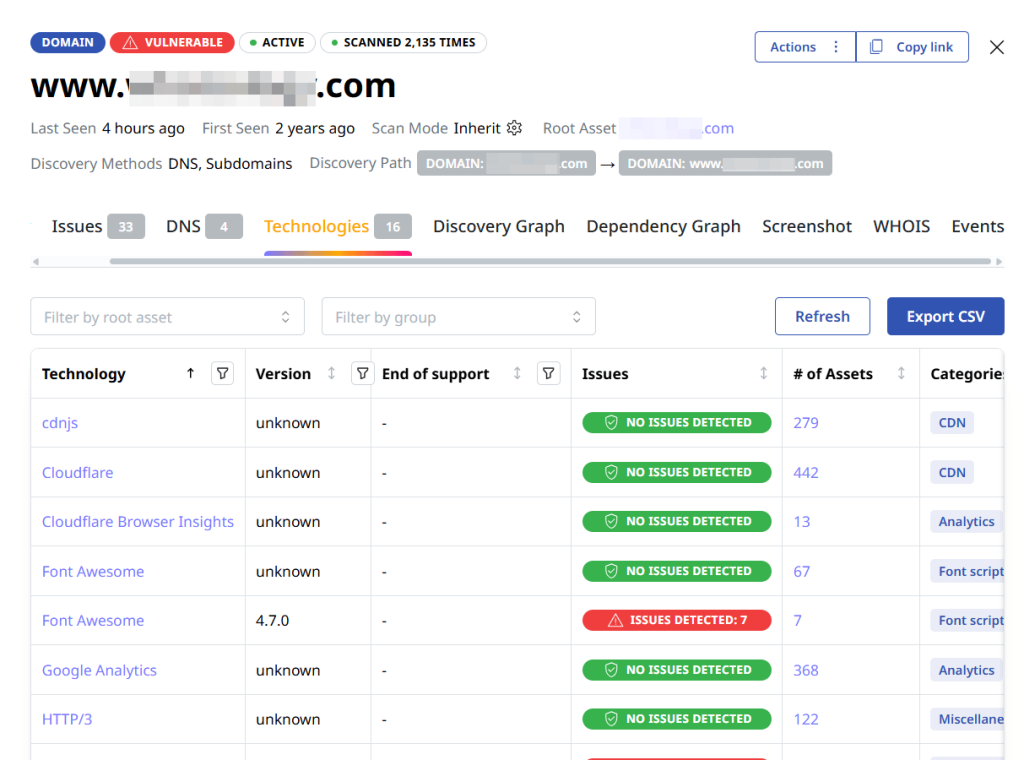
Once an asset is found, asset discovery tools enrich it with more data. For example, if the asset in question is a domain, this data could be the associated IP address, operating system, open ports, SSL certificates, software versions, the cloud provider hosting the associated website, and SaaS services associated with it.
- Correlate and Deduplicate
Using different discovery methods could result in finding the same asset more than once. For example, a discovery tool might find example[.]net through the SAN field of example[.]com’s TLS certificate, and separately find it again through a reverse IP lookup on a seed IP address. Both discoveries point to the same domain, and this step in the discovery process recognizes that and merges the two findings into one record instead of creating two copies of example[.]net in the inventory.
- Validate Existence and Ownership
Not all assets found during discovery are relevant to your organization. An asset might have already been decommissioned, but still have a DNS footprint, or it might belong to a third-party vendor. Validation confirms the asset still exists and belongs to your organization.
- Add Assets to the Inventory
Once validated, an asset gets added to the organization’s asset inventory as a system of record, along with the attributes collected earlier.
- Monitor Continuously
An organization’s environment changes constantly — new assets are created, and old ones get decommissioned. To keep inventory accurate over time, asset discovery needs to run continuously instead of being just a one-time project.
What Are the Main Asset Discovery Methods?
Most IT asset discovery tools combine more than one method, and these are some of the most common ones:
| Method | How it works | Best for | Main limitation |
| Active | Probes assets and networks directly | Detailed, real-time network visibility | Generates traffic that can trigger defenses and disrupt services |
| Passive | Analyzes network traffic, logs, records, and other telemetry without directly probing anything. | Low-impact, continuous monitoring | Misses assets that don’t have observable activity or a footprint in telemetry. |
| Agent-based | Endpoint software gathers and reports data | Deep visibility into managed devices | Requires the agent to be deployed first |
| API-based | Queries SaaS, platform, or cloud APIs | SaaS and cloud environments | Limited to connected sources |
Active Discovery
Active discovery involves probing assets and networks directly using tools that send requests and analyze responses to identify live devices, open ports, and running services. Some techniques only work within a network segment you already have access to, which makes them internal-only. Others scan the public internet, which is how external attack surface management platforms use active scanning to map exposed infrastructure from outside. Below are some examples:
- Ping sweeps (internal): Send ICMP echo requests across a range of IP addresses to see which ones respond to confirm that a live host is present.
- SNMP querying (internal): Queries a device’s Simple Network Management Protocol (SNMP) agent to pull configuration and status data, common on routers, switches, and printers.
- ARP scanning (internal): Sends Address Resolution Protocol (ARP) requests across a local network segment to map which IP addresses correspond to which MAC addresses.
- Port scanning (internal and external): Sends packets to a target port across multiple IP addresses or to a range of ports on a target IP address to see what services might be running on those ports.
- Banner grabbing (internal and external): Connects to an open port and reads the response text a service sends back, which often reveals the software name and version running behind it.
- OS fingerprinting (internal and external): Analyzes details in how a device responds to crafted packets (like how it handles a malformed TCP request) to infer its operating system.
Active discovery gives real-time visibility, but it generates network traffic, which means it can disrupt sensitive systems or get flagged by monitoring tools, so teams typically run active scans during maintenance windows to limit disruption.
Passive Discovery
Passive discovery methods watch network traffic or other data flows instead of probing anything directly. Common techniques include:
- Packet sniffing (internal): Captures and analyzes network traffic as it passes by, without sending anything to the devices involved.
- NetFlow/sFlow analysis (internal and external): Reviews flow data exported by routers and switches, which summarizes who talked to whom and when, without capturing full packet contents.
- DHCP lease monitoring (internal): Watches DHCP requests and lease assignments to catch new devices as they join the network and get an IP address.
- DNS lookup (external): Resolves a domain’s DNS records, like A, MX, or TXT records, to map what infrastructure sits behind it.
- Reverse DNS lookup (external): Looks up the domain name associated with a given IP address by querying its PTR record.
- Certificate transparency (CT) log monitoring (external): Scans public logs of TLS certificates issued to catch new subdomains or hosts tied to an organization’s certificates.
- WHOIS lookup (external): Retrieves public domain registration records, like registrant, registrar, and creation or expiration dates, tied to a domain.
- Reverse WHOIS lookup (external): Finds other domains registered under the same organization, using shared details in the WHOIS record, such as an email address or company name.
Traffic-based techniques (mostly used for discovering internal assets), such as packet sniffing or NetFlow analysis, can only see what’s actively communicating, so they can miss quiet or dormant systems. Record-based techniques (used for discovering external assets), like WHOIS or certificate transparency monitoring, don’t have that limitation since they don’t observe traffic in the first place. Their tradeoff is different, though. They only see assets that leave a public trace, which can result in outdated data.
Agent-Based Discovery
Agent-based discovery relies on software agents installed on endpoints. The agent reports back data about the device it’s running on, including installed software, running processes, patch and configuration status, and hardware specifications.
This method gives ongoing visibility into managed devices, but it only works on systems where an agent can be deployed, so it won’t find shadow IT or anything outside IT’s control. It also comes with some overhead — running an agent on every endpoint has a cost in performance and maintenance.
Where this method shines is continuous, real-time reporting on managed devices. That makes it useful for IT asset management (ITAM) as much as for security, since the same agent data that flags a missing patch can also confirm a license is in use.
API-Based (Cloud) Discovery
API-based discovery queries the APIs of cloud providers, SaaS platforms, and other connected services directly. This is how discovery tools find cloud instances, storage buckets, serverless functions, SaaS accounts, and OAuth grants tied to those accounts.
The catch is that it only covers what’s registered with a connected account. It won’t reveal a cloud resource that was never linked, such as a personal AWS account an employee used for a side project. This method also requires API credentials for each account you want visibility into, so coverage is only as complete as the connected accounts.
Why Is Asset Discovery Important?
Without accurate asset discovery, teams can end up with the difficult task of defending an environment they don’t fully understand. Asset discovery supports several outcomes, including:
- Attack surface coverage: Asset discovery provides visibility into an organization’s IT resources and connected infrastructure that need protection. Security teams cannot implement proper security controls without a good picture of all assets.
- Vulnerability management: IT asset discovery feeds the inventory that vulnerability scans rely on.
- Attack surface management and exposure management: Continuous asset discovery helps organizations keep an up-to-date view of their attack surface and risk exposure.
- Regulatory compliance: IT asset discovery is a compliance requirement of frameworks like NIST CSF, ISO 27001, SOC 2, and PCI DSS, all of which call for an accurate inventory of the systems and data they cover.
- Shadow IT discovery: Asset discovery can uncover unknown assets, including rogue online accounts, cloud instances, applications, and other Internet-facing assets that the IT team did not sanction and that may carry unauthorized privileges. That’s why there’s an overlap between shadow IT discovery tools and asset discovery tools. According to TrendMicro’s research, 74% of organizations have experienced security incidents due to unknown or unmanaged assets.
- Incident response: Knowing what assets exist and how they’re configured speeds up containment during an incident. When responders already have a map of what’s connected to what, they can isolate the right systems fast instead of spending precious time figuring out what’s in scope while an attacker is still moving through the network.
- Operational and cost visibility: Accurate inventories also help IT teams plan capacity, manage licenses, and retire unused resources.
Asset Discovery vs. Asset Inventory vs. IT Asset Management
These three terms are often used together, but they describe different things.
Asset discovery is the process of finding assets within or connected to an organization’s environment. Everything found during that process is used to build or update an asset inventory, which also contains each asset’s attributes.
IT asset management (ITAM) then uses that inventory, along with financial, operational, ownership, licensing, and lifecycle information, to manage those assets over time.
The table below briefly describes these terms:
| Concept | What it is |
| Asset discovery | The process of finding assets that exist in or are connected to an organization’s environment |
| Asset inventory | The record or database of known assets and their relevant attributes |
| ITAM | The broader discipline of managing assets throughout their lifecycle |
To make the distinction more concrete, here’s an example:
- An asset discovery system detects a previously unknown server at a specific IP address and identifies its operating system and exposed services.
- That server is added to the organization’s asset inventory.
- ITAM goes further from there, tracking who owns the server, what it costs, which software licenses apply to it, and when it’s due for replacement or retirement.
In cybersecurity, IT asset discovery also helps reveal assets that have never made it into the official inventory. This is particularly important for externally exposed infrastructure and shadow IT, where relying only on an existing configuration management database (CMDB) or a static asset inventory can leave unknown assets invisible to security teams.
What Are the Challenges of Asset Discovery?
Asset discovery may sound straightforward — just scan your environment and catalog all assets. But there are some challenges that make it difficult in practice.
- Ephemeral cloud assets: Cloud instances can be created and then disappear within minutes, so discovery has to run frequently enough to catch them before they’re already gone.
- Remote and BYOD environments: Devices connecting from outside the traditional network perimeter are harder to track.
- Inaccessible network segments: Some parts of the environment, like isolated OT networks, are hard to reach with standard discovery methods.
- Incomplete data sources: No single method or source covers everything, so gaps in coverage are common if teams use tools that focus only on one area.
- Duplicate or inconsistent records. The same asset found by different tools or methods can end up looking like several different assets.
- False positives: External discovery in particular can flag assets that turn out to be decommissioned, misattributed, or unrelated to the organization.
- Ownership attribution: Finding an asset is one thing, but figuring out whether it really belongs to the organization — and who’s responsible for it — is often the harder problem.
Asset Discovery Best Practices
Some consistent practices help make IT asset discovery programs more effective:
- Combine multiple discovery methods instead of relying on just one so you’ll have wider coverage.
- Unify your asset inventory even if cloud, internal, and external discovery run through different tools. Feed the findings of each tool to a single inventory or CMDB.
- Run discovery continuously rather than as a one-time project.
- Validate ownership for every asset you find.
- Integrate discovery findings with your CMDB and other security tools.
- Automatically flag new or unknown assets as soon as they are detected.
- Measure discovery coverage over time so you know how complete your inventory actually is. Learn how to compute the metric here, which is also tracked in vulnerability management.
How Attaxion Can Help
As an exposure management platform, Attaxion supports external attack surface management and is built around continuous agentless discovery.
It scans internet-facing environments the way an attacker would, mapping domains, subdomains, IP addresses, cloud services, and other internet-facing infrastructure, including the shadow IT and forgotten assets that traditional discovery tools tend to miss.
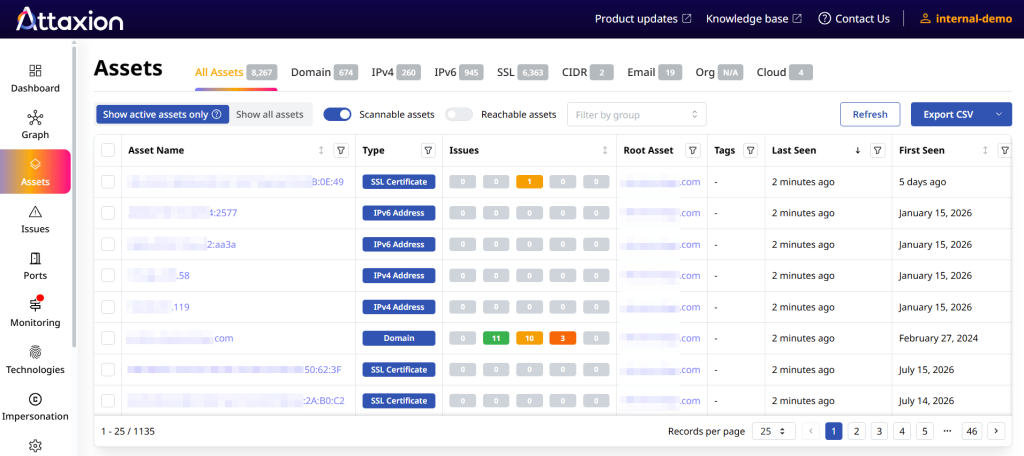
Attaxion enriches discovered assets with WHOIS, IP, and DNS context, enabling dependency mapping. It then scans assets for vulnerabilities and misconfigurations, so security teams get a current, prioritized view of what needs attention.
Discover your external assets with Attaxion — start a free 30-day trial.